How to Install Wireguard VPN on Debian 12
Introduction
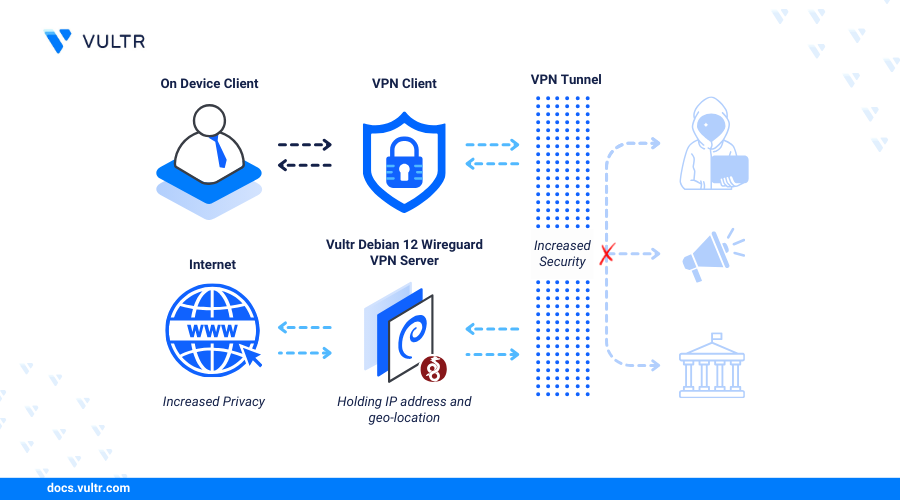
WireGuard is a modern, efficient, and secure VPN protocol that overcomes the complexities and performance issues related to old VPN solutions. WireGuard enables every peer to function as a server and a client by allowing each peer to have unique keys and configurations. This architecture facilitates direct, encrypted communication between peers without relying on a centralized server.
This article shows you how to install WireGuard on Debian 12.
Prerequisites
Before you begin:
- Deploy two Debian 12 instances on Vultr to use as the VPN server and client respectively.
- Access the WireGuard server using SSH as a non-root user with sudo privileges.
- Update the server.
Install WireGuard
WireGuard is available in the default repositories on Debian 12. Follow the steps below to install WireGuard using the Advanced Package Tool (APT).
Update the server's package index.
CONSOLEInstall WireGuard.
CONSOLEView the WireGuard version on your server.
CONSOLEOutput:
Configure WireGuard
WireGuard uses key pairs to create secure and encrypted connections between peers. Each WireGuard client or server uses a unique private key to generate a public key. A private key signs outgoing traffic and decrypts incoming traffic, while a public key encrypts traffic from other peers when sending traffic to the server. Follow the steps below to create a new WireGuard interface and generate the server key pair.
Generate a new private key for the WireGuard server and store it in the
/etc/wireguard/directory.CONSOLEOutput:
Change the private key file permissions to give the directory owner read privileges.
CONSOLEUse the private key to generate a new public key.
CONSOLEOutput:
Create a new WireGuard interface configuration file
wg0.confunder the/etc/wireguard/directory.CONSOLEAdd the following configurations to the file. Replace
+E0z2nYOezr5oHWASuMJJEGXTouBrdyhK7DKxyE8iEQ=with the private key you generated earlier.INISave and close the file.
The above configuration creates a new
wg0WireGuard interface and10.0.0.1as the tunnel address. Within the configuration:[Interface]: Creates a new WireGuard interface.PrivateKey: Sets the WireGuard server's private key.Address: Sets the WireGuard interface's IP address when communicating with connected peers. The10.0.0.0/24network address enables a subnet that supports up to 256 addresses, while10.0.0.1is the WireGuard interface address.ListenPort: Specifies the UDP port the WireGuard interface should use to listen for incoming VPN connections. The value51820is the default port number for WireGuard interfaces.
Generate a new WireGuard client private key.
CONSOLEOutput:
Generate a new public key using the WireGuard client's private key.
CONSOLEOutput:
Open the WireGuard server
wg0interface configuration file.CONSOLEAdd the following WireGuard client configurations at the end of the file. Replace
n2nSd/oOVlukX4wx2y4p5IPF3XETA/3gOjI8zSUpFlg=with the actual client's public key you generated earlierINISave and close the file.
The above WireGuard configuration directives enable a new WireGuard client to connect to the interface with the tunnel IP address
10.0.0.2.View your WireGuard server's public IP address.
CONSOLEOutput:
The WireGuard server uses the public IP address
192.0.2.4based on the aboveenp1s0interface information output.Create a new WireGuard client configuration file.
CONSOLEAdd the following configurations to the file. Replace
gHVZgu6TsxQj+SRQl9OK8gIJ8w71h4v7mdUUIxb/7nw=with your actual client private key andO1fiUPB73tNIJGPgsjuA613N3VBuA/KuQp8xPjwJwnU=with your WireGuard server's public key values you generated earlier.INISave and close the file.
The above client configuration creates a new tunnel connection using
192.0.2.4as the WireGuard server's public IP address. Within the configuration:[Interface]: Creates a new WireGuard client interface.PrivateKey: Sets the WireGuard private key when encrypting traffic.Address: Sets the WireGuard client's IP address when connecting to the VPN tunnel.[Peer]: Enables the WireGuard server remote peer configuration when establishing tunnel connections.PublicKey: Sets the WireGuard server's public key.Endpoint: Specifies the target WireGuard server public IP address and port.AllowedIPs: Specifies the client IP network connections to allow through the VPN tunnel. When set to0.0.0.0/0, the WireGuard client forwards all network traffic to the VPN tunnel.
Manage WireGuard VPN System Processes
WireGuard uses the wg-quick utility to manage all tunnel interfaces on a server. Follow the steps below to manage the wg0 WireGuard interface and enable tunnel connections to the server.
Enable the WireGuard interface to automatically start at boot.
CONSOLEOutput:
Start the WireGuard interface.
CONSOLEView the WireGuard interface status and verify that it's active.
CONSOLEOutput:
Stop the WireGuard interface.
CONSOLERestart the WireGuard interface.
CONSOLE
Set Up Firewall Rules
WireGuard listens for incoming tunnel connection requests on the default UDP port 51820 specified in your interface configuration. Follow the steps below to configure the Uncomplicated Firewall (UFW) active on Vultr Debian servers by default to allow network connections to the WireGuard interface.
View the UFW status and verify that it's active.
CONSOLEOutput:
Allow WireGuard UDP port
51820through the firewall.CONSOLEOutput:
Reload UFW to apply changes.
CONSOLEOutput:
View the UFW status and verify that port
51820is allowed through the firewall configuration.CONSOLEYour output should be similar to the one below:
Connect Client Devices to the WireGuard VPN Server
A WireGuard VPN server accepts network connections from all clients with valid keypairs to connect to the tunnel interface. Follow the steps below to access your Debian 12 WireGuard client instance and connect to the WireGuard server.
Access your Debian 12 WireGuard client instance using SSH.
CONSOLEUpdate the server's package information index.
CONSOLEInstall WireGuard.
CONSOLEDownload the client configuration from your WireGuard server using a secure file transfer protocol such as SCP and save it as
wg0.conf.CONSOLEStart the
wg0VPN interface using your client configuration file.CONSOLEOutput:
View the WireGuard tunnel status and verify that the client connects to the WireGuard server.
CONSOLEYour output should be similar to the one below.
Test the connection to your WireGuard server's tunnel address
10.0.0.1using the Ping utility.CONSOLEYour output should be similar to the one below when the connection is successful.
Conclusion
You have installed WireGuard on a Debian 12 and created tunnel interfaces to enable network connections between peers. You can create multiple WireGuard interfaces with unique ports and connect multiple clients using valid key pairs on the server.


0 Comments
Be the first to comment and share your perspective with the community.